Senior engineers configure, tune and run Cloudflare, Fastly, Bunny, Amazon CloudFront, Google Cloud CDN, Akamai and Azure Front Door for your websites, apps and APIs, so every user is served from the nearest edge. Fully managed, average response under 8 minutes, 24/7.
Average response, across all tickets, 24/7
L1–L3 engineers on shift around the clock
Major CDN platforms managed, single or multi-CDN
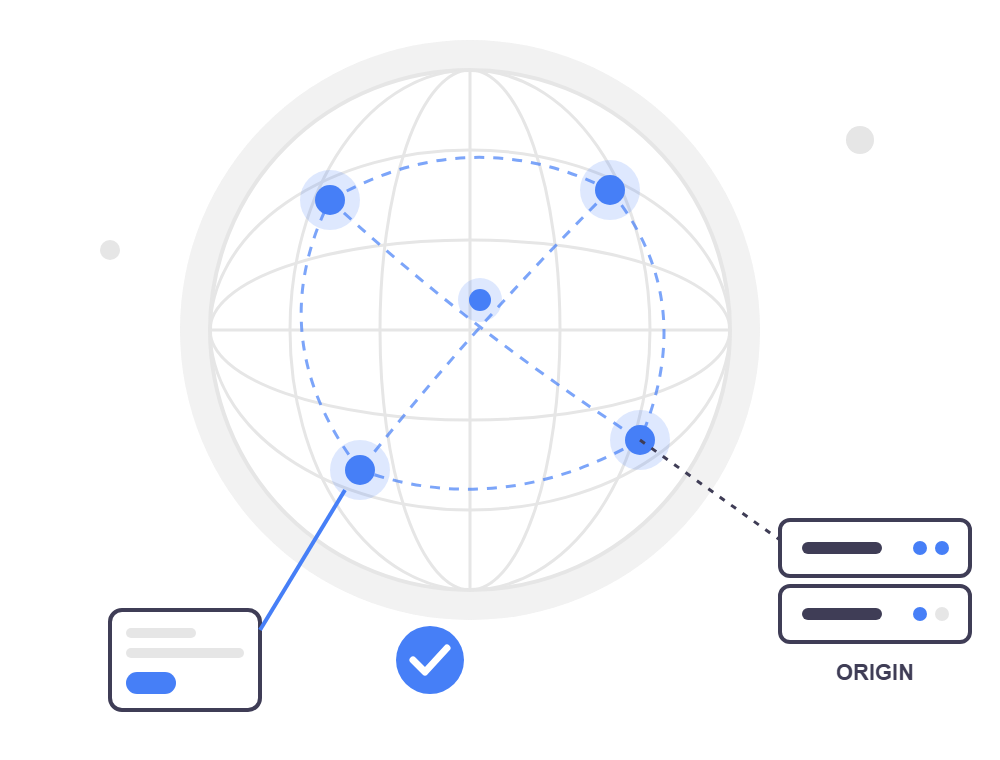
TechProvidence provides managed CDN services across every major provider. Senior engineers choose, configure, tune and secure your content delivery network so websites, applications and APIs load fast everywhere, and respond to incidents 24/7.
We work with the platform that suits your traffic, stack and budget, and run several side by side when you need it.
Cache rules, Tiered Cache, Argo Smart Routing, Workers, WAF, bot management and Zero Trust, set up and tuned for your application.
VCL and Compute services, origin shielding, surrogate-key purging in milliseconds, real-time logging and Next-Gen WAF.
Pull zones, Perma-Cache, Bunny Optimizer image delivery, Edge Scripting and storage, for fast delivery at a predictable cost.
Cache and origin request policies, Origin Shield, CloudFront Functions and Lambda@Edge, AWS WAF and VPC origins for private backends.
Cloud CDN behind Google Cloud load balancers and Media CDN for video and large downloads, with Cloud Armor in front.
Enterprise delivery on Akamai, and Azure Front Door Standard or Premium, including moves off the retiring classic Azure tiers.
From choosing a provider to answering the 3 a.m. alert, one team owns your edge.
Single or multi-CDN designs based on where your users are, what you serve and what it costs, with no lock-in to one vendor.
Cache keys, TTLs, tiered caching and origin shielding tuned for a higher hit ratio and a lower time to first byte worldwide.
Redirects, headers, A/B routing, geolocation and authentication at the edge with Workers, Compute, CloudFront Functions or Edge Scripting.
WAF and DDoS protection, bot and rate-limit rules, modern TLS, and origin lockdown so attackers cannot bypass the CDN.
Zero-downtime moves between providers, DNS traffic steering, health-checked failover and consistent configuration on every CDN.
Latency, hit ratio and error rates by region, alerting and incident response, plus regular reviews of egress and plan costs.
Running two CDNs protects you from a provider outage and lets each region use the fastest network. It also doubles the configuration, purging and billing. We keep every CDN consistent, steer traffic with health-checked DNS, and fail over automatically.
consistent rules, purges and certificates across every provider
Turning on a CDN takes minutes. Getting the lowest latency from it takes expertise. Most setups we review cache too little because of cookies and query strings, send every miss straight to the origin, leave the origin open to direct attacks, or pay for traffic that should never have left the edge. Each provider names and configures these things differently, so the knowledge rarely transfers between platforms. Our engineers work across all of them every day.
We recommend the CDN that fits your users, workload and budget, and tell you when the one you already have is the right choice.
Configuration as code with Terraform or the provider API where possible, staged rollout, and a written rollback for every change.
Monitored and tuned as your traffic grows, with one named technical lead and on-call engineers responding in under 8 minutes on average.
A CDN is only as fast as the origin behind it. We also provide Varnish cache support, NGINX support and performance tuning, managed AWS services, managed Google Cloud, WordPress hosting and clustering and Magento hosting.
We measure latency and hit ratio by region, review your CDN and origin configuration, and check how exposed your origin is.
Provider choice, cache and security rules are written as code with a test plan and a rollback, agreed with you in advance.
Changes go to a staging hostname or a small share of traffic first, with short DNS TTLs so we can switch back in minutes.
24/7 monitoring, a monthly performance and cost report, and continuous tuning as your traffic changes.
Every engagement is scoped to your environment and backed by a written agreement.
We own your edge end to end: CDN configuration, security rules, certificates, purging, monitoring and on-call, under a monthly retainer.
We work alongside your in-house team, covering nights, weekends, escalations and specialist CDN work.
Latency audits, CDN selection, provider migrations and multi-CDN builds, delivered to a fixed scope.
Expert CDN management under your brand, for agencies and hosting companies.
A senior engineer reviews your CDN setup, latency and costs. You receive a written report with prioritised recommendations.
We work from read-only access to your CDN dashboard or API, or through a named, logged account you control.
Cloudflare, Fastly, Bunny (bunny.net), Amazon CloudFront, Google Cloud CDN and Media CDN, Akamai and Azure Front Door. We manage single-CDN setups and multi-CDN setups that combine them.
It depends on where your users are, what you serve and your budget. Cloudflare is a strong all-rounder with built-in security, Fastly suits highly programmable sites that need instant purging, Bunny delivers well at a low cost, and CloudFront or Google Cloud CDN fit naturally when your application already runs on AWS or Google Cloud. We recommend after measuring, not before.
Yes. Even when a response cannot be cached, the CDN terminates TLS close to the user, reuses connections to your origin and can route around congested networks. Where it is safe, we also cache API responses and page fragments for short periods.
Yes. We run two or more CDNs with consistent rules, purging and certificates, and steer traffic with health-checked DNS so a provider outage fails over automatically.
Yes. We rebuild the configuration on the new provider, test it on a staging hostname, then move traffic gradually with a rollback ready. This includes moves off Azure Front Door (classic) and Azure CDN Standard from Microsoft (classic) before their 2027 retirement dates.
Often. A higher cache hit ratio means less traffic from your origin and fewer origin servers, and the right plan or provider can cost much less. We report costs monthly so you can see the effect.
Logged-in sessions, carts, checkout, account pages and authenticated API calls bypass the cache by rule, and we test those rules before and after every change.
Yes. L1–L3 engineers are on shift around the clock, and our average response is under 8 minutes across all tickets. Enterprise contracts can carry a written SLA.
Book the complimentary CDN review or request a proposal. After a short discovery call, we send a written plan scoped to your environment.
Cloudflare, Fastly, bunny.net, Amazon CloudFront, Google Cloud CDN, Akamai and Azure Front Door are trademarks of their respective owners. TechProvidence is not affiliated with these providers.
Our engineers keep your CDN tuned, secured and watched around the clock, whichever providers you use.